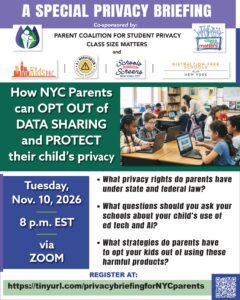
On Tuesday November 10 at 8 PM EST, we are hosting a special briefing on what privacy rights NYC parents have under state and federal law, as well as what questions parents should be asking your principals about screen time, ed tech and AI assigned to your children, as well as strategies you can use to opt them out of the use of these products. Please register here. Co-sponsored by Class Size Matters, the Parent Coalition for Student Privacy, the AI Moratorium Coalition, Schools Beyond Screens and Distraction-Free Schools.
All posts by admin
Ed tech products approved for NYC school use (updated 11.2.2026)
Updated November 2, 2026
Here is the updated spreadsheet of now 118 ed tech products, including five high school AI pilots, that DOE has approved for principal or district use, though more are added each week. We will keep updating this list going forward, which is otherwise unavailable to parents as its sit in an area of the DOE website that only school administrators can access.
These products have supposedly been vetted for privacy — though we know that the DOE vetting process called ERMA is inadequate and has led to numerous breaches and the commercial use of student data prohibited by law. Moreover, as far as we know, none of these products have been shown to have any educational value.
More caveats and concerns with the way in which these products are noncompliant with the state privacy law here, including privacy policies that explicitly say they data-mine personal student information for product improvement and other commercial purposes. Many like PowerSchool are facing major lawsuits for their re-disclosure of the data to unauthorized third parties, and have suffered massive breaches because of lax security practices.
Finally, there are likely other ed tech products that DOE central has approved for use not on this list. A pdf of the list is here and below.
Problematic ed tech products approved by DOE — & how you can help!
October 15, 2026 [updated October 20, 2026 with more approved products]
On Tuesday, DOE officials posted on an internal, private section of their website for school administrators a list of 94 107 ed tech products that they can purchase for use in their schools. They said that these products have gone through their (ineffective) privacy vetting process and are consistent with their new AI/screen time policy.
They cautioned, however, that not every piece of software on the list is approved for use in every school or grade — and that schools and districts “must ensure that use aligns with the AI and Screen Time Policy, including grade-level-specific guidance and requirements.” They also said that more products may be added to this list over time. Moreover, there are likely other ed tech products that DOE central has made available for student use, such as problematic Google products pre-loaded on their Chromebooks.
As noted on this spreadsheet [updated 10.20.26], eleven thirteen of the ed tech products on the list have no privacy agreements on the DOE webpage, where such agreements by law are supposed to be displayed for all vendors with access to student personal information.
We have serious concerns with other products on the list, even though they have privacy agreements on the DOE webpage, including the PowerSchool Student Information System (SIS), which in December 2024 breached the personal data of millions of students nationwide, including thousands of current and former NYC students.
The data that was obtained by hackers included student names, addresses, their medical information, disability status, IEPs, and more. Over fifty class action lawsuits were filed in different districts now consolidated into a single massive litigation, charging the company and their majority owner Bain Capital with offshoring cybersecurity, engineering, and IT functions to irresponsible subcontractors, whose shoddy practices allowed cybercriminals to access the data.
Other highly problematic PowerSchool products on the DOE approved list include Naviance, which NYC high schools will still be allowed to assign to students for college counseling and application purposes, despite the fact that the company recently agreed to pay $17.25 million to settle a class action lawsuit to families whose kids’ sensitive and personal data was improperly disclosed to third parties through the Naviance platform.
In addition, PowerSchool now faces another national class-action lawsuit on privacy grounds, claiming that its products illegally monetize student and family data, including Naviance and Schoology – another program on the DOE approved list.
Even before the PowerSchool breach and these lawsuits were filed, we strongly advocated with the DOE to stop allowing schools to use PowerSchool products, noting how the Privacy agreement that is still posted on the DOE webpage asserts that the company will comply with federal and state privacy laws only when the company considers them “commercially reasonable.” See the screenshot below.
Since the massive PowerSchool breach, the filing of these lawsuits, and the Naviance settlement occurred, it is simply outrageous that the DOE intends to let schools continue to use these untrustworthy products that put their students’ privacy and safety at risk.
Also on the new list of approved DOE ed tech products are the five AI high school pilot programs. We have now analyzed the public-facing Privacy Policies of these programs, showing that three of the five say that they data-mine student information to improve their products, in violation of the NY student privacy law, Ed Law 2d.
Another of the pilots, Intel AI-Ready Schools, has no public-facing Privacy Policy, though its general Privacy Policy allows for data mining for product improvement, as well as for advertising and marketing purposes – also contrary to the law.
The only AI pilot company where the use of student data for product improvement is specifically prohibited is Brisk, though we have other concerns about that program, which gives immediate and continuous feedback to students while they are in the process of writing, which could undermine their confidence, cognitive development, and independent writing skills. Brisk also uses a chatbot, which would appear to contradict the city’s claim that “Companion chatbots will be prohibited across all grades.”
Here are three steps you can take to challenge the use of these risky ed tech programs:
- Please sign our AI Moratorium petition demanding the cancellation of the high school AI pilots. The privacy and learning of our students should not be put at risk—especially when three of these companies appear to use their personal data in ways that violate the law.
- If you are a parent of a high school student, urge your principal and/or School Leadership Team not to apply to be a pilot. This is a decision that the SLT should be in charge of since they are in responsible for creating the school’s Comprehensive Education Plan.
- Finally, all parents should ask the principal of their children’s schools which ed tech products will be assigned to students and which their teachers will be allowed to use. Parents have a right to know every company and product with potential access to their children’s personal information, according to Ed Law 2D. If they tell you they will be assigning or utilizing a product that isn’t on the approved list, ask why.
We are planning to hold a briefing very soon on the privacy rights that NYC parents have under the law as well as strategies they can use to opt out of these programs.
Thanks, Leonie
Statement on the NYS Comptroller’s audit of NYC’s Privacy and Security of Student Data
May 4, 2025
The audit from the State Comptroller’s office released today confirms what many NYC advocates have long known: the privacy policies and practices of the NYC Dept. of Education are sloppy, irresponsible and show a lack of concern for keeping students’ personal information safe from breach and misuse. This makes DOE’s insistent push to rapidly expand the use of Artificial Intelligence tools in our schools unwarranted, given how these tools represent an even greater risk to student privacy and safety.
Even more troubling is the DOE contemptuous response to the auditors’ findings and recommendations to improve their processes, dismissing nearly each one as unfounded. Altogether, the audit’s findings reinforce the lack of trust felt by many in DOE’s competence and caring when it comes to protecting student privacy.
The audit’s findings put in question the AI guidance’s assurances on DOE’s ability to keep student data safe
In the recent DOE AI guidance, they repeat over and over that student privacy is rigorously protected through a vetting process called ERMA (Enterprise Request Management Application). Yet the findings in this audit show that DOE’s privacy processes are inherently defective. The DOE’s lack of responsiveness and willingness to improve their privacy policies provide yet more evidence that their rush to expand the use of AI in our schools is reckless. AI products represent a special risk to student privacy as many data-mine personal data to improve their products, which violates the state student privacy law, Ed Law 2D, the NY State Student Privacy law passed by the legislature in 2014.
The audit’s findings, as well as repeated data breaches of NYC student data and its illegal use for commercial purposes reveal the inadequacy of the DOE’s privacy vetting process. As a member of the Chancellor’s AI Working Group, I along with other members proposed additional safeguards. These included independent privacy impact assessments, data security audits, and tests for algorithmic bias that should be required for any educational product using AI. DOE rejected all these recommendations. Additional problems with the recently released AI guidance, including DOE’s refusal to rigorously comply with the state privacy law, are described in our critique here.
The findings confirm DOE’s failure to properly control and safeguard personal student information
The auditors discovered that DOE maintains no central records as to which vendors and other third parties have access to student personal information, and that they maintain no written policies covering data classification, risk assessment, or backup and recovery, as required by the NIST data security framework specified by Ed Law 2D.
In their response, DOE officials claim that this conclusion is false, and that they are “able to determine which SIS or other applications that consume student data are in use by a given school or office.” Yet just last week, on April 28, 2026, the DOE privacy office confirmed in an email to a parent that “at this time, there is no Central list of every educational technology tool used by each school.”
Moreover, according to Ed Law 2D, it is every parent’s right to know which vendors have access to their children’s data, and to receive a copy of the data held by those vendors within 45 days of their request. Yet this right is chronically violated by DOE officials, and when parents do receive data files from their vendors, the files can be empty of information.
There are more than 700 companies and other third parties that have access to personal student data according to the DOE website, though the number of the ed tech programs used is likely greater, as some vendors provide schools with more than one product. The number of products collecting and processing student data has steadily increased each year, and is even now even more rapidly growing, as DOE adds new products with AI functionality to be used in classrooms throughout the city.
Delays in recognizing and reporting breaches
Because DOE officials do not know which schools use which products, they are unable to ensure that when data breaches occur, they are able to inform affected families within the legally required timeline or identify which data elements may have been exposed.
The auditors reported that there were at least 141 breaches of NYC personal student data between January 5, 2023 through February 27, 2025, and in 48% of cases, the DOE reported them to NYSED past the legal deadline of 10 days. In at least one case, it took over 460 days. DOE also missed the 60 day deadline to inform parents that their children’s data had been breached in at least 11% of the time. [Note: 60 days is in itself too long; NY law requires breach notification by private businesses and state agencies within 30 days.]
The Illuminate breach and problems with their privacy agreement
Some privacy vendor agreements are never even posted online in violation of the law – like that of Illuminate, which exposed the data of more than a million NYC current and former students in 2022, and yet whose privacy agreement was posted online only after the breach occurred. Even then, the agreement hinted that the data was not always encrypted, contrary to the requirements of the law, which turned out to be the case.
The Illuminate example also shows that DOE does not independently investigate breaches but instead relies on the unreliable reporting of vendors concerning the number and identity of students affected. After the data of more than 800,000 current and former NYC students was breached by Illuminate between late December 2021 and early January 2022, their families were not notified by DOE until March 25, 2022.
Even worse, in May 2024, more than two years after the breach, a second round of notifications to families revealed that about 380,000 more students and former students also had their information exposed. This was also seven months after Illuminate had informed DOE of the additional students involved – far exceeding the 60 day deadline in the law, according to the information on the DOE website, which states that they started looking into this matter only after being told by Illuminate that more students were affected in October 2023. This put additional students and former students at risk of identity theft and more, and unable to promptly acquire the insurance and credit monitoring offered by the vendor for free.
The PowerSchool breach and problems with their privacy agreement
After the massive nationwide breach of the PowerSchool student information system occurred in late December 2024, parents throughout the country and elsewhere in the state were informed of the breach in early January 2025. Yet at that time, DOE told a reporter they were still looking into whether any NYC schools or students were affected.
In fact, DOE refused to confirm which schools were involved even after Daily News reported on their names on February 6, 2025, from information relayed by the State Education Department. Only after the Daily News reported on this did parents whose children attended these schools receive emails saying DOE was still looking into this matter. It was not until April 2025 that DOE confirmed to parents that their children’s data had been breached, long past the 60-day deadline in the law.
To this day, the DOE has refused to post the names of the NYC schools affected by the PowerSchool breach on the webpage that reports on data security incidents, despite guidance from the NYSED that they should do so promptly, to alert the thousands of former students whose data was also exposed and put at risk of identity theft and worse.
As the former NYSED Chief Privacy Officer Louise de Candia wrote on Feb.3, 2025, “ There is no doubt in my mind that PowerSchool violated Education Law Section 2-d and Part 121 of the regulations which require compliance with NIST CSF as well as reasonable administrative, technical and physical safeguards to protect the security, confidentiality and integrity of PII.”
And yet DOE continues to allow NYC schools to use as many as 16 other privacy-invasive PowerSchool products, including Naviance, which is employed in many if not most New York high schools for college guidance purposes. This is despite the fact that in 2022, it was reported that Naviance targeted ads for colleges on its student-facing platform disguised as objective recommendations and was shown to allow colleges to discriminate by race by targeting ads only to white students.
More recently, it was announced that PowerSchool had agreed to settle a class action lawsuit alleging that the Naviance platform contained ad tracking technology that transmitted a wide range of student data to Google, Microsoft and a company called Heap, including their names, ID numbers, graduation years, demographic information, photographs and survey responses, as well as their private communications with teachers. This would violate not only state privacy laws but also the federal wiretapping statute. Even now, the DOE has refused to tell parents or students about the Naviance agreement or inform them they can apply for a portion of the $17.25 million settlement.
The fact that the Illuminate and PowerSchool breaches exposed the data of many thousands of NYC students who had long graduated or otherwise left the system also shows that the data minimization and deletion by vendors required by Ed Lawa 2D is not enforced by DOE. More background here.
To make things worse, the PowerSchool privacy agreement still posted on the DOE website is clearly non-compliant with the law, as it says that the company will only conform to the privacy requirements in federal and state law or in their contract with DOE when it is “commercially reasonable.”
Other problems highlighted in the audit and the DOE’s official response
The Comptroller’s office also found significant weaknesses in DOE’s technical data security controls that should be corrected, including “issues with system monitoring, unsupported systems, and firewalls.” Understandably, the auditors only communicated the details of these security weaknesses to DOE in a separate confidential report. In their response, DOE makes no commitment to address these technical problems, but instead says that they would address them separately, within the confidential report.
In its response, DOE claims to have made “several improvements to its privacy practices and policies,” including updating the Chancellor’s Regulation A-820 to “restrict the use of “directory information.”
In fact, the recent amendment to the Chancellor’s Regulation weakened the protections for student data, by redefining a wide and essentially unlimited range of personal student information, including but not limited to their names, addresses, telephone numbers, email addresses, photographs, grade level, participation in activities and sports, and more, as directory data that can be shared with third parties, even when they are not providing services to schools. Only an unreliable parent opt out process was provided to prevent these disclosures from occurring.
Finally, the auditors also revealed that DOE officials took an inordinate time to respond to their requests; and that documentation requests took over five months to fulfill, while requests for meetings took two months to schedule.
Leonie Haimson is the co-chair of the Parent Coalition for Student Privacy, a member of the NYSED Data Privacy Advisory Committee, the Chancellor’s Data Privacy Working Group and the Chancellor’s AI Working Group
###
Problems with the NYC Dept. of Education’s AI Guidance
April 25, 2026
This one-page summary is also posted as a pdf here. The DOE deadline for feedback is May 8, 2026 via their survey at on.nyc.gov/AiFeedbackNYCPS
The Guidance itself is posted here; our more detailed critique is here and embedded below, along with a partial list of AI programs currently used in NYC schools. Also posted online is an annotated pdf of the AI Guidance with our comments.
On the survey, feel free to borrow any of the below points, provide your own, or write, “I urge you to implement a 2-year moratorium, so rigorous protections can be developed to prevent harm to students, including their privacy, their cognitive development, creativity, mental health and the environment – none of which this guidance sufficiently addresses.”
1: Lack of public input
Despite claims to the contrary, the DOE has not been responsive to the concerns of parents or the community in its determination to rapidly expand the use of AI in the classroom. Nor did this AI guidance document receive significant input from those most affected, either students, teachers or parents. Neither the members of the Data Privacy Working Group nor the AI Working Group appointed by the Chancellor Ramos were allowed to provide comment to the guidance before it was released– despite repeated assurances to the contrary from DOE officials. And from the DOE’s actions, it is apparent that they intend to continue the rapid expansion of AI whatever the official feedback process consists of in the coming weeks.
2: There is no transparency about which AI products can be used, or that when AI is used at all, there needs to be full disclosure
The DOE AI guidance provides no clarity or transparency about which AI products can be used with students, or those that have gone through the DOE privacy vetting process known as ERMA. While the AI Working Group asked for the names of approved products that are currently used in schools, DOE officials refused, saying they had non-disclosure agreements with their vendors. Perhaps as a result, teachers continue to assign students to use off-the-shelf AI products that data-mine personal student information to improve their products –a commercial use specifically prohibited by the state student privacy law. Regardless of which AI tool is used by teachers or students, there needs to be full disclosure as to which program is being employed and for what purpose.
3: The AI guidance fails to rigorously protect student privacy
The DOE privacy vetting process is ineffective and primarily composed of a series of boxes which vendors are merely asked to check off in order to be approved. This process has not worked to protect student privacy, as shown by recent breaches of personal information of over one million NYC students and the continued illegal use of student data for commercial purposes, as indicated by recent court settlements and consent decrees. Although AI represents an even higher documented risk to student privacy and safety, the DOE has developed no additional privacy safeguards for its use – despite recommendations from the Chancellor’s appointed AI working group and others to strengthen this process.
4: The AI guidance is inadequate, often confusing and even contradictory as to how teachers and students should use the technology
Instead, if offers a traffic light metaphor, with most potential applications in the “yellow” category, meaning used with caution, leaving it up to teachers to use their best judgement in most of these cases, without giving them clear direction. Other directives are contradictory – as to whether AI can be used for student placement. One bullet point says no; the other says placement decisions can be overridden by teachers or students – but how can that be done if there’s no clarity that the decision was made by AI in the first place? Many of the thorniest questions as to the proper and safe use of AI are punted, to be dealt with at some unspecified time in the future.
5: There is no attempt in the AI guidance to address many of the most serious concerns that parents and educators have about AI use
Growing evidence shows how AI usage can undermine students’ cognitive development, their acquisition of fundamental skills, weaken their critical thinking and creativity, worsen their mental health challenges, and exacerbate climate change. Yet the guidance does not attempt to address any of those risks. Nor does the guidance provide any answers when it comes to the algorithmic biases often embedded in AI, or the technology’s rampant factual errors, called hallucinations. It also has nothing to say about AI’s tendency towards sycophancy— in which AI chatbots have been designed to agree with the user’s opinions, flatter them, and encourage them in whatever course they are considering, no matter how dangerous it may be. All of these are well-known problems with AI and in the latter case, it has even contributed to teen suicide, according to several ongoing lawsuits. The DOE claims that it will address some of these issues by the end of the year, but there needs to be a moratorium now, so that rigorous protections can be established with public input before the use of AI is further expanded in our schools.
For more information, email us at info@studentprivacymatters.org or check our website at www.studentprivacymatters.org Also, please sign the AI Moratorium Coalition petition at https://tinyurl.com/petitionAImoratorium to be kept up to date on this issue.
“